Security & Compliance
Security governance. Active assessment. Clear accountability.
Motenza Capital maintains its security and compliance program in Drata Advanced. This Trust Center gives clients, lenders, and business partners one place to review our program, understand current framework readiness, and request supporting information.
Program foundations
Our 25 approved security policies cover access management, data protection, vendor risk, incident response, business continuity, and workforce responsibilities. Policy owners, renewal dates, control mappings, and supporting evidence are organized in Drata for ongoing review.
Framework readiness — work in progress
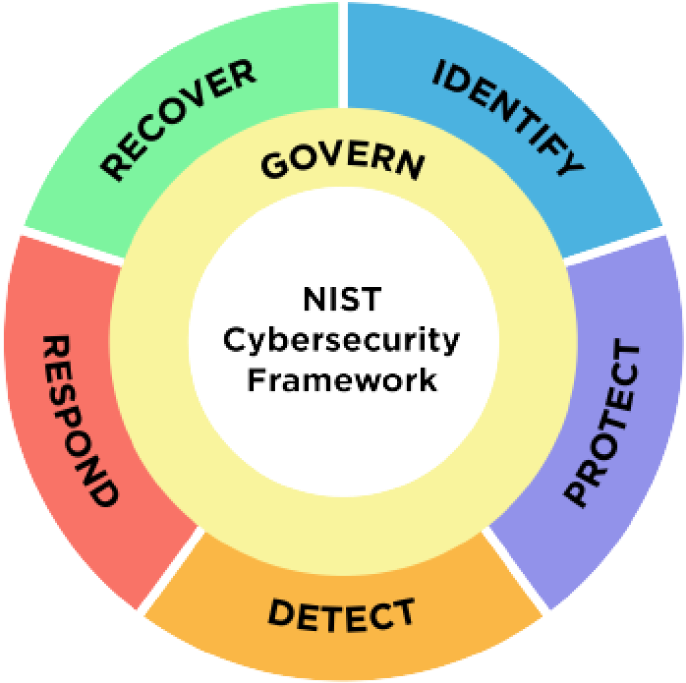
- NIST CSF 2.0: active internal assessment.
- SOC 2: control and evidence readiness preparation.
- ISO/IEC 27001: internal mapping currently references the 2013 edition; see the framework card for scope.
The badges indicate readiness work, not completed certification or an issued audit report. Open each badge for its scope and dated status.
A clear path for partner due diligence
- Review the Security Overview and program summaries below.
- Select Get access to request supporting information. Requests and restricted documents remain subject to review.
- For a focused review, contact compliance@motenzacapital.com with your organization, review scope, and required materials.
Status reviewed: September 26, 2026.
Data Security
Responsible information handling is a defined part of Motenza's security program. Approved policies cover data classification, protection, retention, and encryption, supported by documented ownership and review dates in Drata. This workstream connects information governance with the current NIST CSF 2.0 assessment. Personal-information practices are described in the Privacy Policy linked below.
Access Control
Access governance is supported by approved System Access Control and Password policies. Named owners and review dates are maintained in Drata, providing a documented structure for access responsibilities and authentication requirements. This workstream forms part of Motenza's ongoing security governance and NIST CSF 2.0 assessment.
Corporate Security
Clear responsibilities are built into Motenza's policy program. Approved Information Security, Acceptable Use, and Code of Conduct documents set expectations for working with company systems and information. These policies are assigned to personnel in Drata, with ownership and renewal dates recorded for ongoing oversight.
Incident Response
Incident preparedness is an established program workstream. Motenza maintains an approved Incident Response Plan with documented ownership and review dates in Drata. The plan supports a structured approach to incident handling and coordinated review. Security concerns can be raised directly with compliance@motenzacapital.com.
Risk Management
Motenza's security program includes approved Risk Assessment and Vendor Management policies. These provide a consistent structure for considering security risks, third-party dependencies, and review priorities. Policy documentation and supporting evidence are organized in Drata as part of the ongoing NIST CSF 2.0 assessment.
BC/DR
Operational resilience is addressed through approved Business Continuity, Disaster Recovery, and Backup documents. Named owners and renewal dates are maintained in Drata to support program oversight. This workstream connects disruption planning and recovery responsibilities with Motenza's broader security governance and assessment process.